capture the flag
Sometimes the best way to improve one's security standing is to pick a target to defend.
One file, with every protection, every lock, with the least-privileged ACL attached, whose paper trail is non-existent, whose location is hidden beneath layers of obscurity and encryption. In addition to being a DevSecOps project, the lab is also organized as a capture-the-flag challenge.
The choice for Domain Name was not an arbitrary one. It is called the Pendragon Lab because buried in the depths of the most secure regions of this lab, lies the Pendragon.
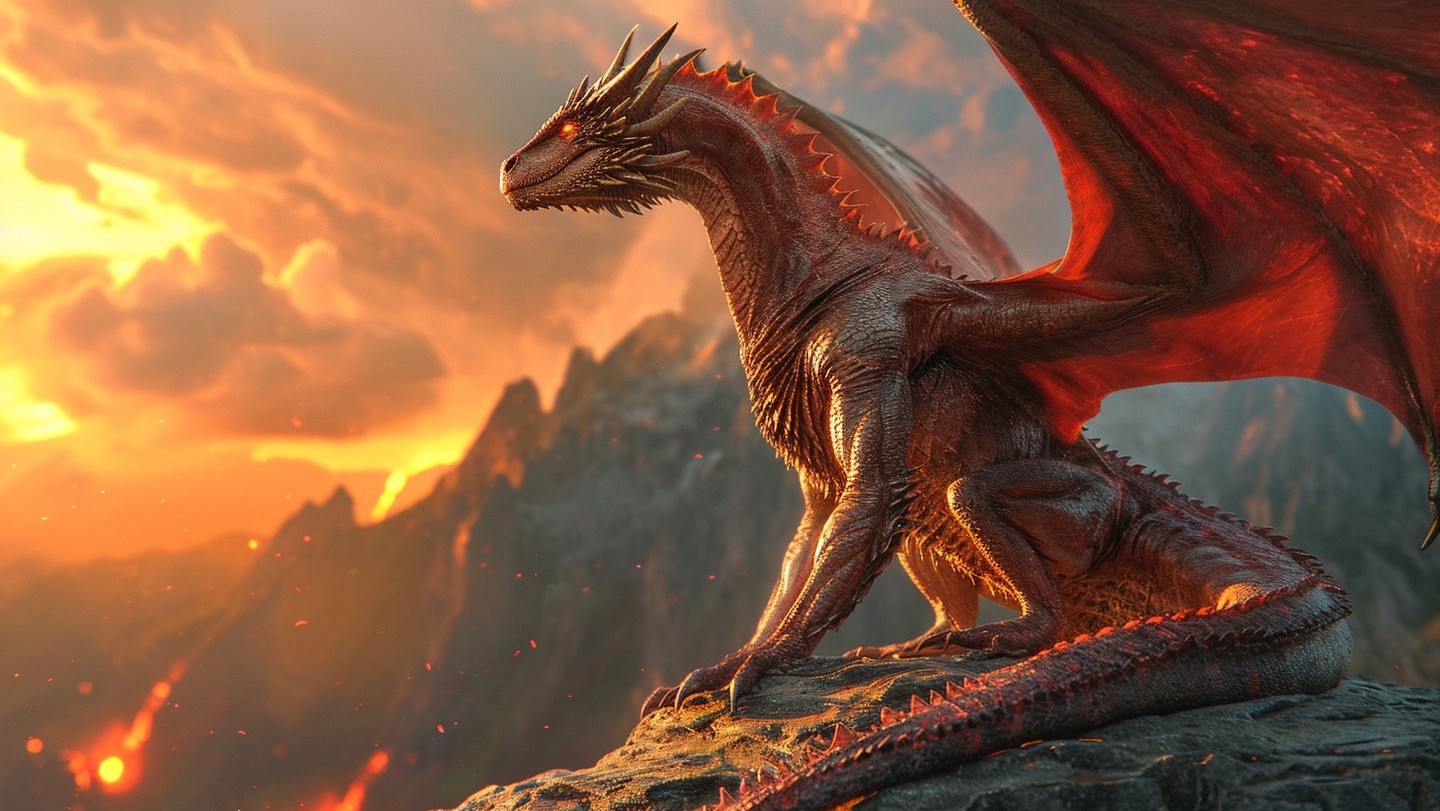 The Red Dragon
pendragon.jpg
The file itself is just a JPG image of the one you see above. You might have recognized the logo being used around this docs page and in many other places around the lab. The Red Dragon is the mascot you could say but more specifically, it is the target.
Only the most worthy may succeed here.
I invite you to utilize your maximum skillset in finding the Pendragon and acquiring its sha512 checksum to confirm its authenticity. If I've done my job right, it will be far from easy.
To confirm receipt of the real Pendragon, here are the last 10 characters of the checksum you seek :
d986dea04f
Through the docs portal, there is enough information to piece together where and how to start. And if you're thinking of just copying and pasting the image above into your local checksum generator, do you really think I would make it that easy?
The image binary data has an embedded ASCII message within it which generates a unique checksum from the one provided in the image above but you should know what you're looking for.
And if you do manage to complete this nigh-impossible task, the feedback you provide goes to hardening the platform even further; it's the best way in fact to find the vulnerabilities you don't know to look for - let someone else find them.
So good luck and happy hunting, traveler.
The Red Dragon is among you.